Automated Remediation

Remove risky access automatically. Prove every fix.
Sentra turns classification into enforcement. Clear-cut exposures, like a confidential file shared publicly, are fixed automatically, down to one link or one user. Ambiguous cases go to the data owner. Every change is logged with the policy behind it.
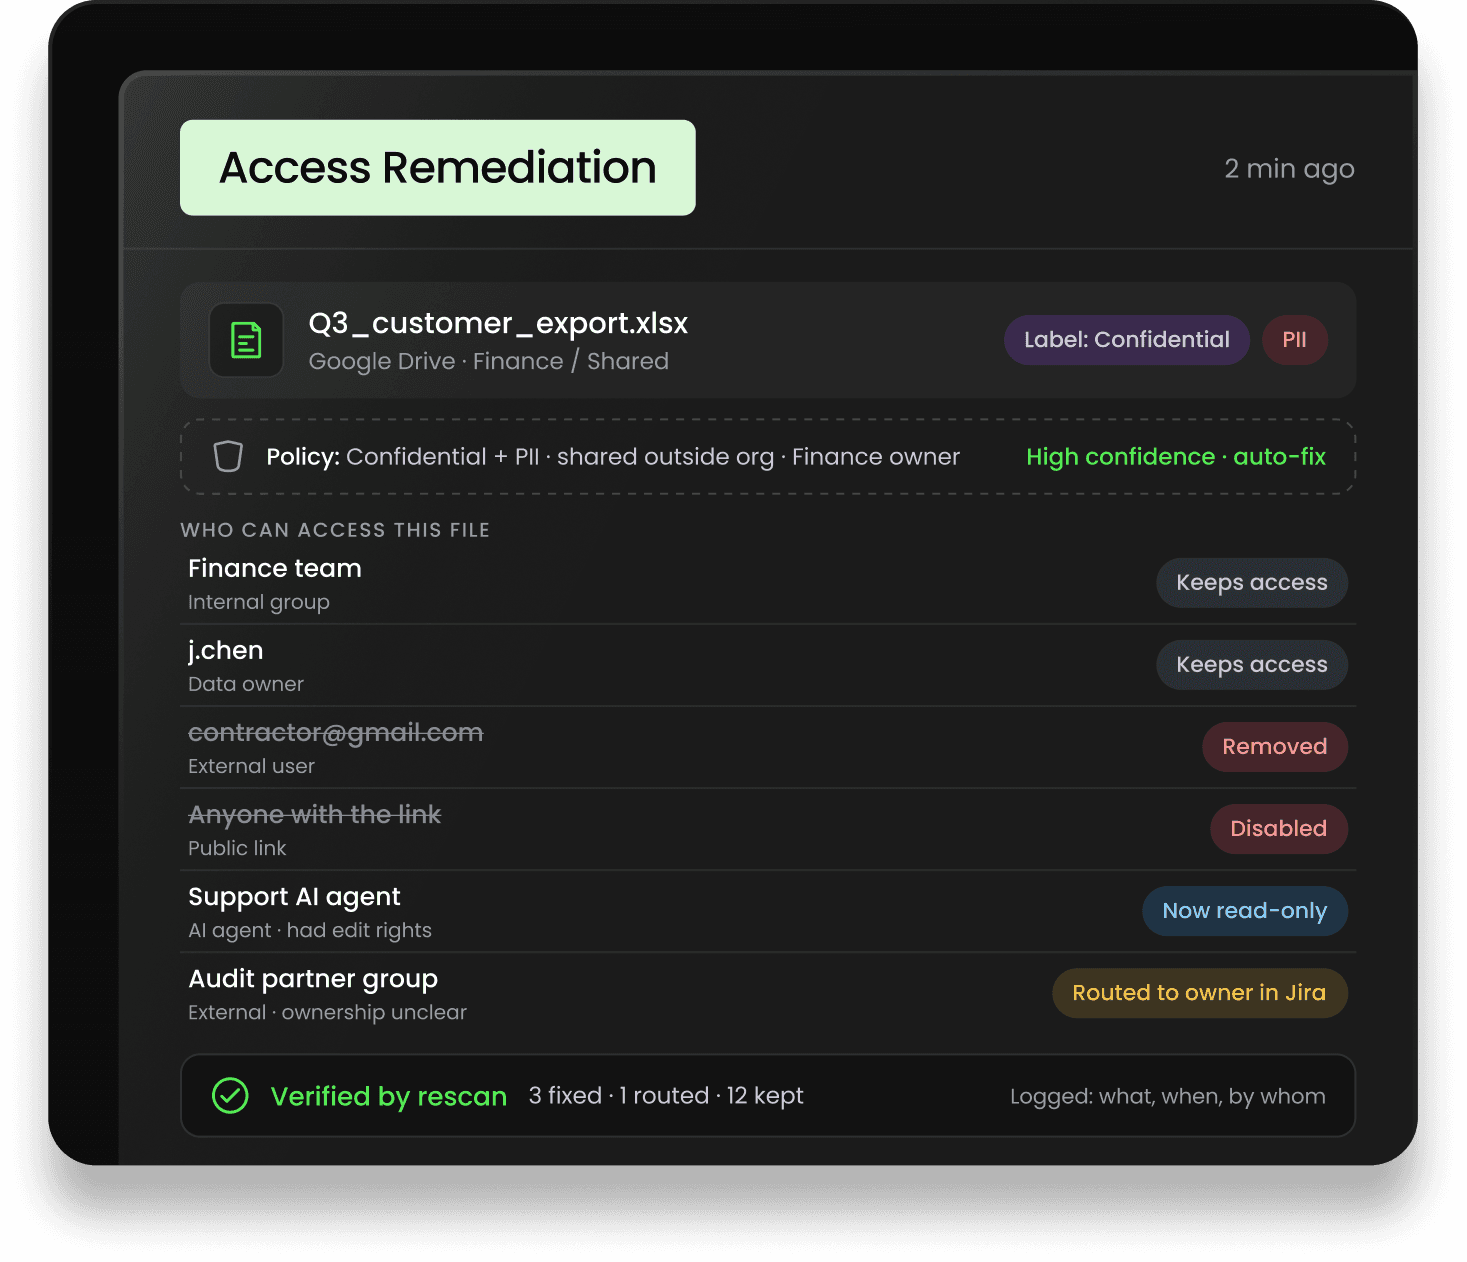
Access Remediation

Findings pile up. Access stays open.

Alert volume

With thousands of findings in a manual queue, the riskiest exposures stay open longest.

Access outlives its purpose

Public links, external shares and old permissions stay open long after anyone needs them.

Fixes wait on other teams

The change belongs to a data owner or IT, so a simple revoke takes weeks.

No record of what changed

When an auditor asks who fixed what and when, the answer is spread across tickets, consoles and spreadsheets.

Close data risk automatically,with a record of every change

Automatic actions at scale

Set a policy once and Sentra acts on every match: disable public links, remove external users, revoke excess permissions, quarantine files or delete redundant copies.

Access removal, down to one identity

Remove only the access that creates exposure, such as one external user, one public link or one overprivileged AI agent. Everything else stays intact, and you preview the change first.

Owners fix what they own

Route judgment calls to the data owner with the context to act, in Slack, Teams, Jira or ServiceNow, and track every issue to closure.

Activity audit on sensitive data

See who and what read, edited, shared or changed permissions on sensitive data, including AI agents. Every automatic and manual fix is logged for investigations.

From exposure to closed, automatically

Detect

Continuous scans surface new exposure.

Prioritize

Ranked by sensitivity, access and AI reach, with a plain-language reason.

Act

Policies trigger the fix automatically, or route it to the owner.

Verify and record

A rescan confirms closure, and every action is logged for audit.

Acts where your data lives,routes where your teams work

Microsoft Teams
Amazon Web Services
Jira
ServiceNow
Google Cloud
Microsoft SharePoint
Slack
Microsoft Teams
Amazon Web Services
Jira
ServiceNow
Google Cloud
Microsoft SharePoint
Slack

Seven targeted fixes, no broad revocation

ActionWhat happens
Remove external accessOne external user, one file or dataset
Disable public linksTurn off one URL open to the internet
Restrict sharing scopeBroadly shared file becomes internal-only
Revoke over-privilegeExcess rights for a person, service or AI agent
Quarantine dataMove high-risk files where users can't reach them
Delete redundant copiesRemove duplicate and obsolete data
Notify data ownersRoute to the owning team with policy context

Secure your data for the agentic era.