It finds every sensitive dataset across cloud, SaaS, on-prem and AI services, shows which people and AI agents can reach it, and keeps it locked down as AI spreads.
See every data store and AI surface — and exactly what each copilot or agent can reach — before you roll it out. No blind spots. No assumptions. One authoritative inventory across the full AI attack surface.
How Sentra delivers complete visibility.
Petabyte-scale architecture
Billions of objects, enumerated cloud-natively. In-environment classification. No wasted compute or expense. No scan failures.
Smart Sampling & metadata-driven clustering
Sample structured data by like metadata type to be statistically representative. Fully scan unstructured, human content. Highly efficient and tunable.
Incremental delta rescans
After the initial scan, only data changes get scanned. Coverage stays updated. No full re-scans, no operational drag. Sustainable at scale.
AI Attack Surface Mapping
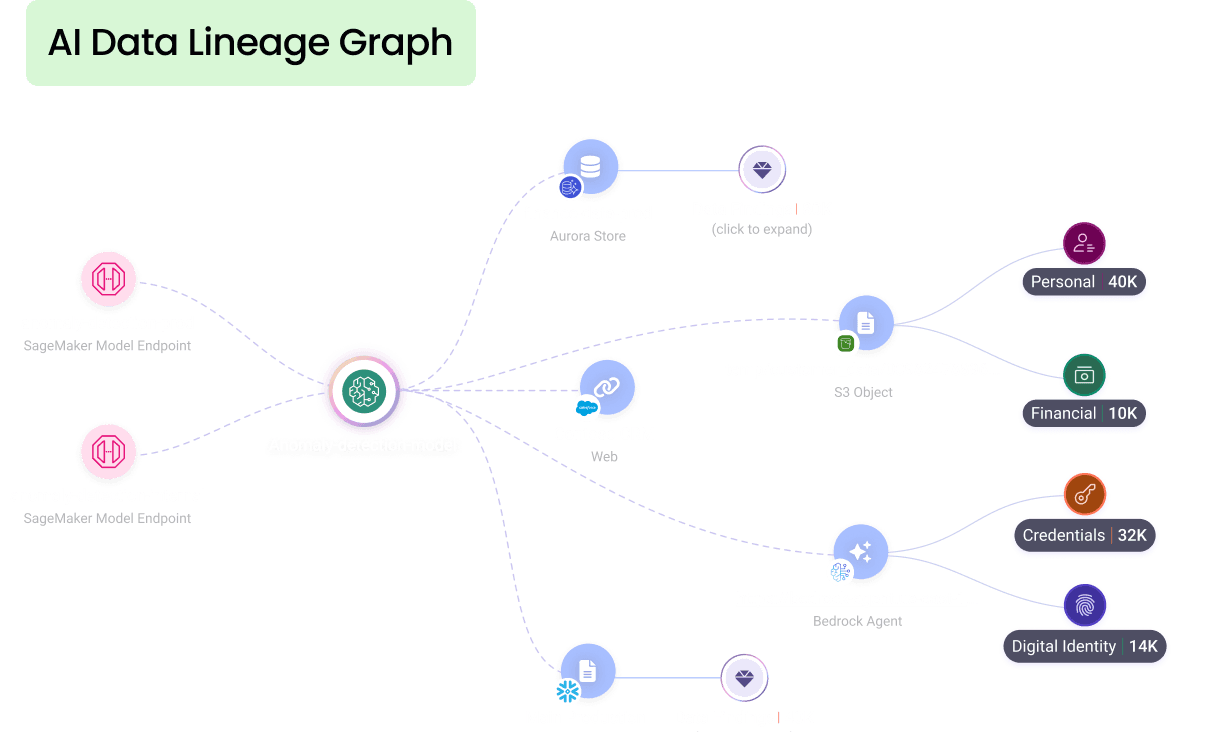
Every copilot, agent, and model mapped. Every exposure path traced. See full attack surface, before it's a problem.
Shadow data detection
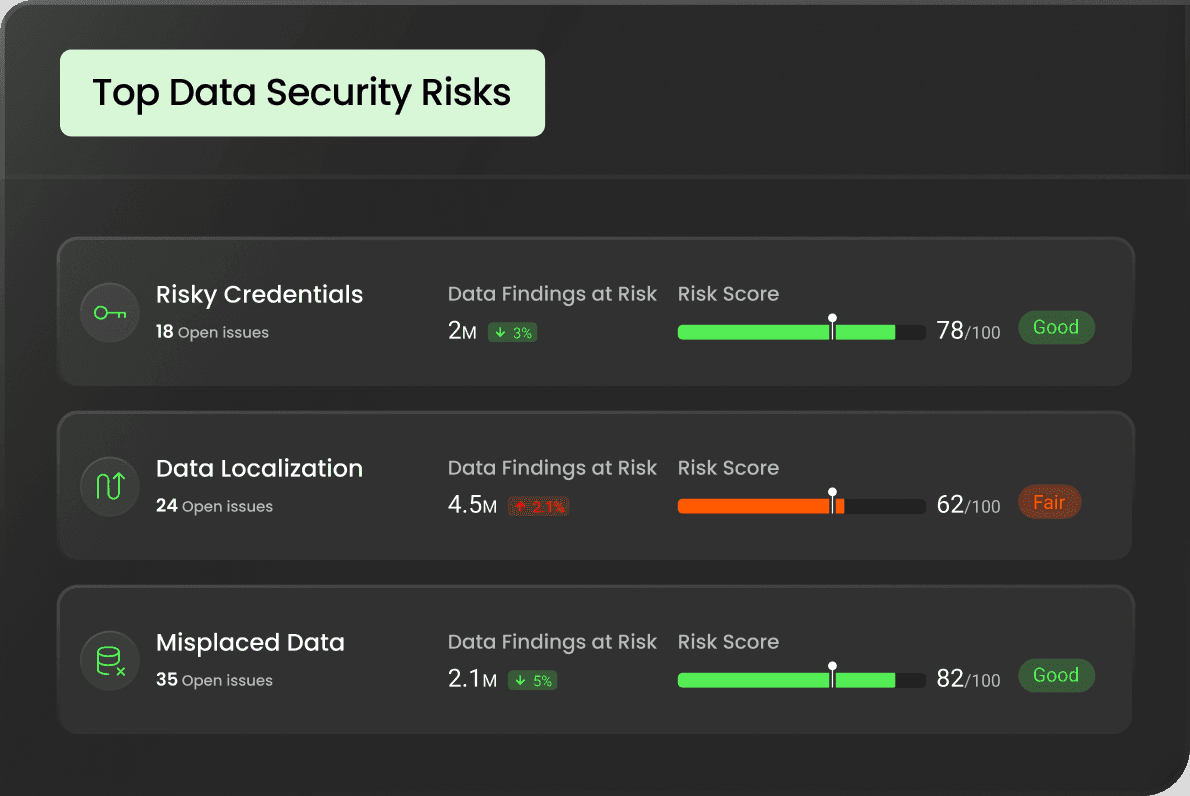
Forgotten buckets, ungoverned SharePoint, abandoned stores, stale dev copies and database backups—know data risks before audit, not after.
98%+ Accurate AI-driven Classification
Get context, not just patterns.
A contract vs. report, PHI vs. test data, production vs. development. Insight to act with confidence.
AI Data Hygiene
AI doesn't care if your data is stale. You should. Continuously remove shadow, stale, and toxic data from AI pipelines, RAG indexes, and knowledge bases — improving risk posture, compliance, and economics simultaneously.
How Sentra executes data hygiene — continuously.
Discover and classify first
Scanning metadata inventories first establishes an accurate scanning plan, and identifies entitlement exposure before any data security improvement occurs.
Deduplicate
Redundant and partially duplicate records identified, linked, and risk evaluated. Non-authoritative copies archived or deleted.
Enforce lifecycle policies
Automated retention policies, with legal holds honored. Unstructured versions resolved to a single governed copy.
Mask and redact sensitive data
PII, regulated data, and toxic structured content is masked, redacted, or tokenized at the source before it feeds any AI pipeline.
Hygiene that never stops
As new data arrives and AI pipelines evolve, Sentra maintains the hygiene baseline automatically. No quarterly cleanup campaigns required.
AI Identity & Access
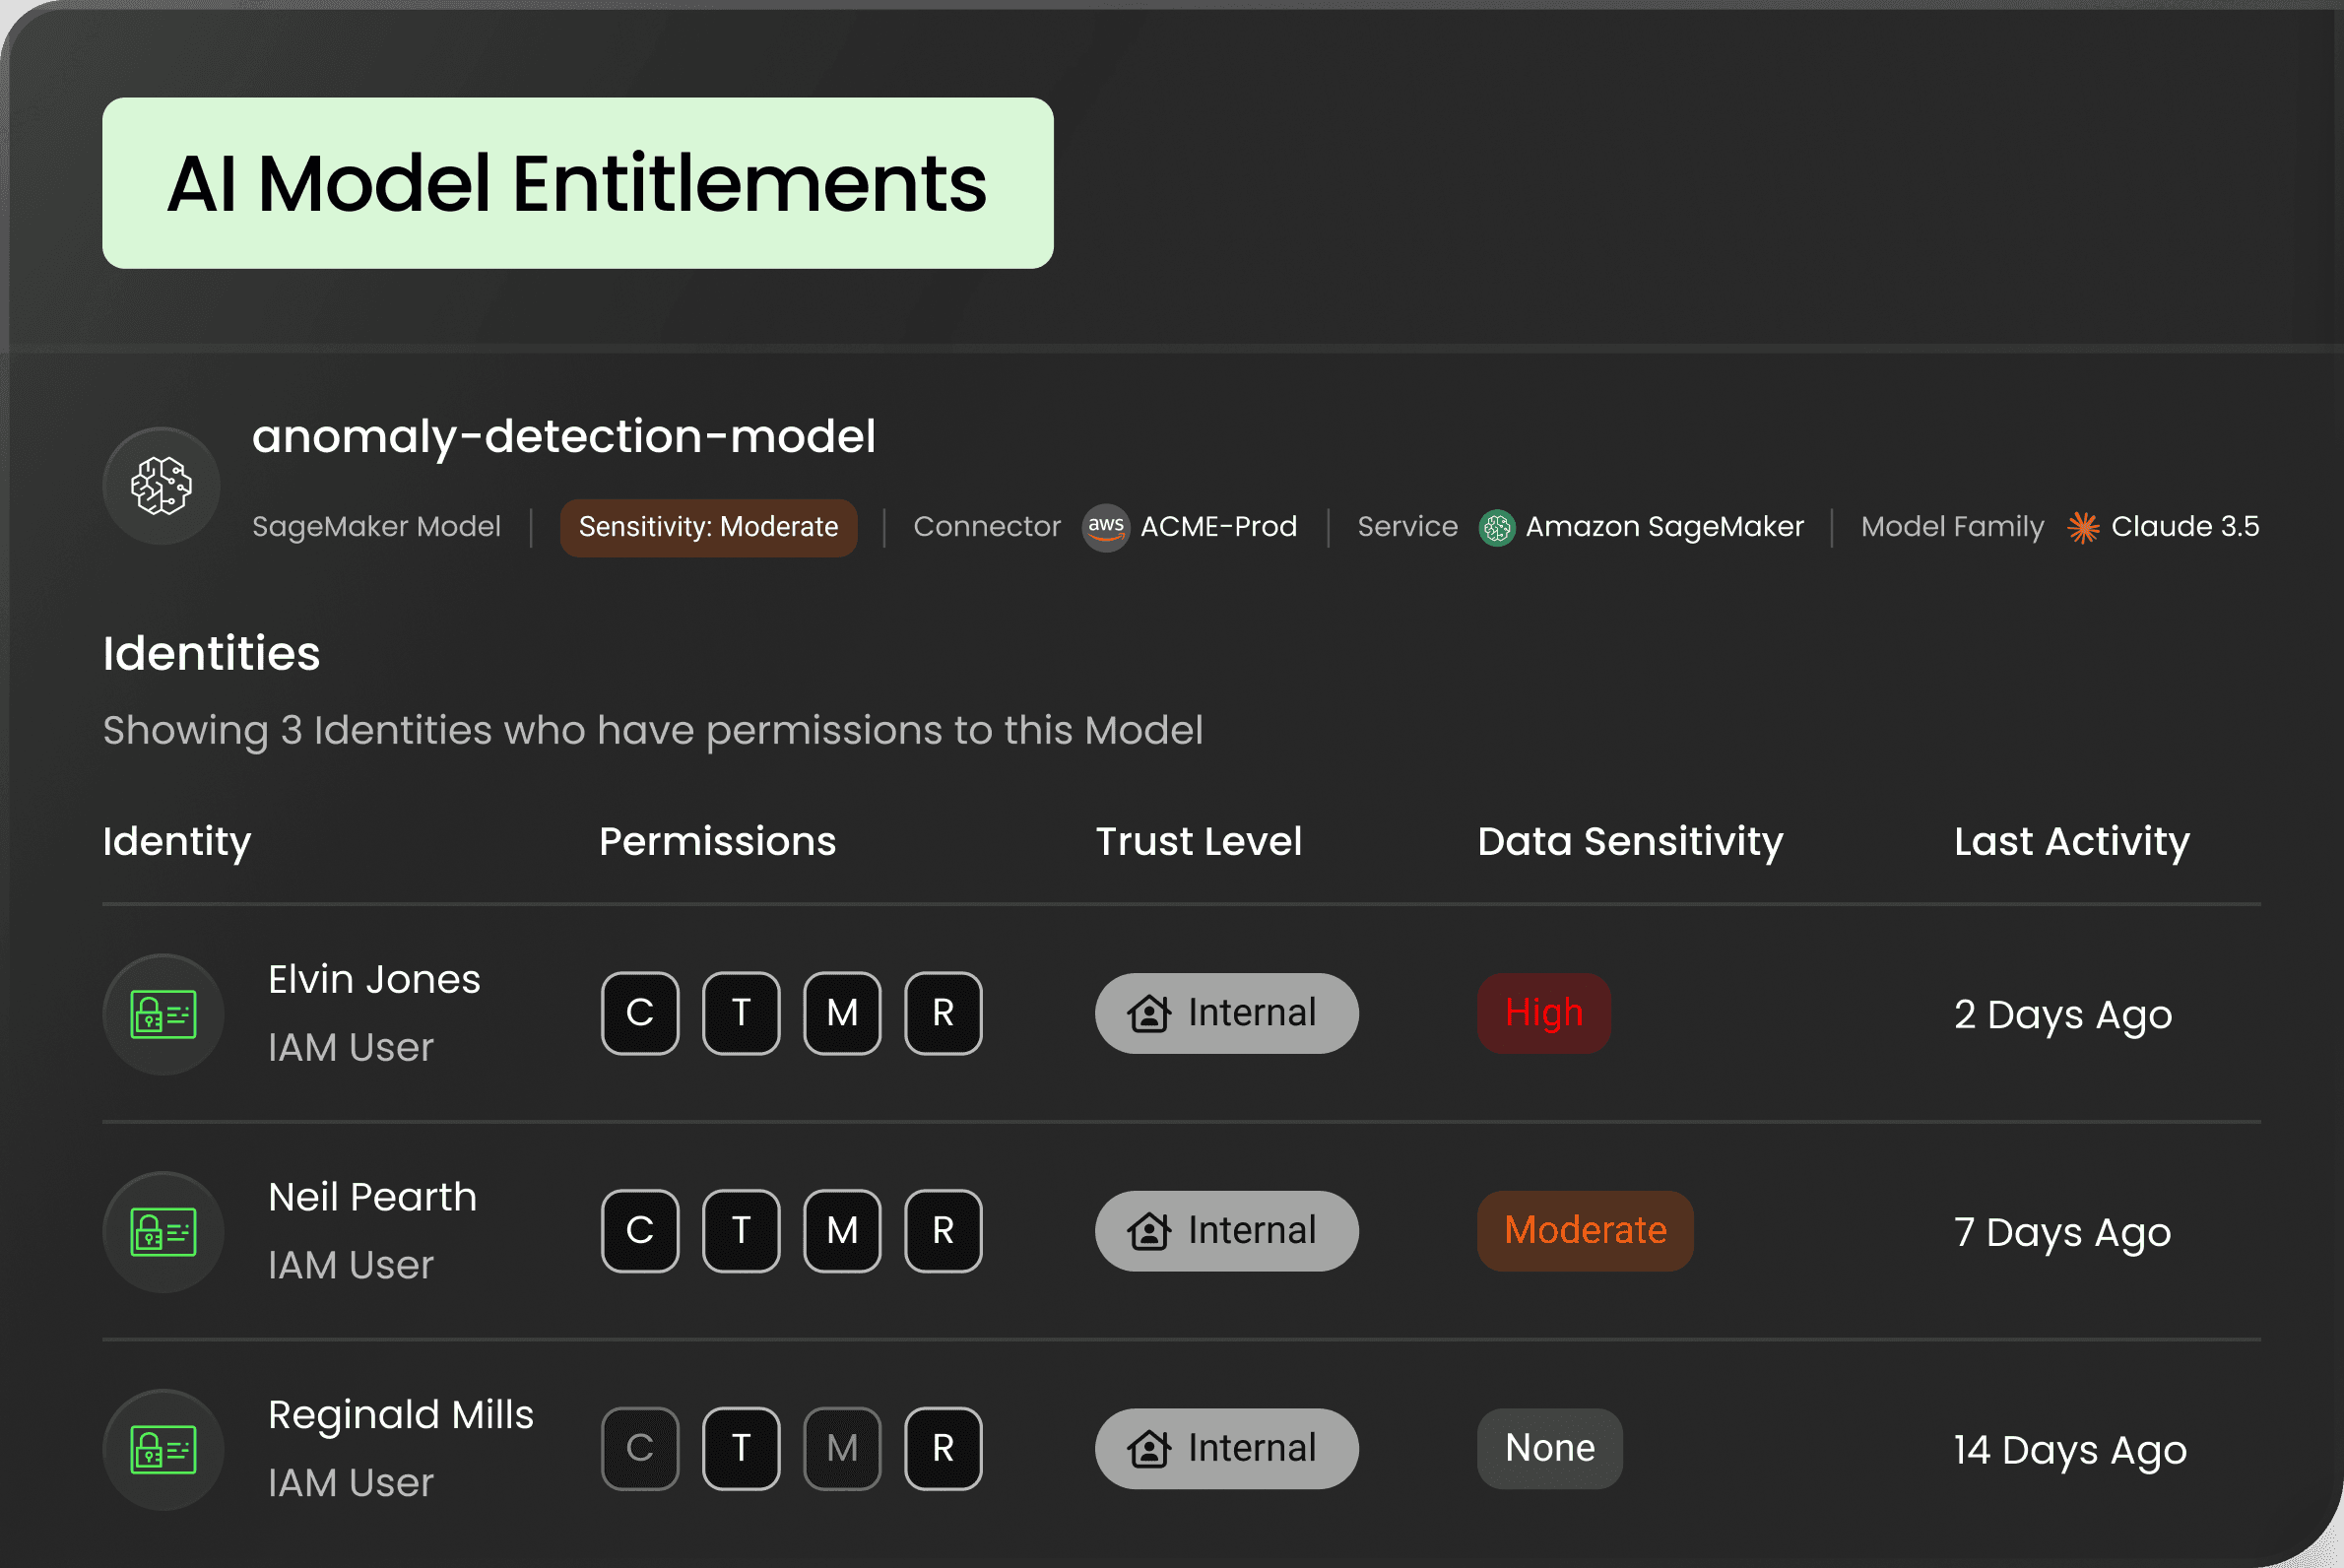
Make entitlements follow the data — so every user and AI agent sees only what they're entitled to, across both the data plane and the AI plane.
How Sentra controls permissions — to govern at the data and AI layer.
AI agent access
governance
Consistent governance model across both data and AI planes, controlling and monitoring what data AI can access.
Lineage-driven
access map
Data, identities, service principals, AI agents all connected. Entitlements follow the data, not the application.
Follow access through AI
When data moves anywhere — from knowledge bases to RAG indexes — access is reconciled.
One authority across estate
Unified policy drives access enforcement for safer rollout of copilots and agents. No drift between policy and reality.
Shadow AI DLP
Microsoft Copilot, ChatGPT, Claude, Gemini, and hundreds of other AI tools are now part of everyday work. Sentra Shadow AI DLP combines Shadow AI Discovery with browser-based data protection to discover AI usage and prevent sensitive data from being shared with AI. Powered by the business context and intelligence of the AI Data Readiness Platform.
How Sentra enables secure AI adoption.
Discover AI
Usage
Automatically identify how employees use AI across the organization. Gain visibility into AI activity, uncover Shadow AI, and understand where sensitive data may be at risk.
Understand what data matters
Inspect prompts, pasted text, and uploaded files using Sentra's business-aware data classification. Detect sensitive data based on context, not just keywords or patterns.
Prevent sensitive data exposure
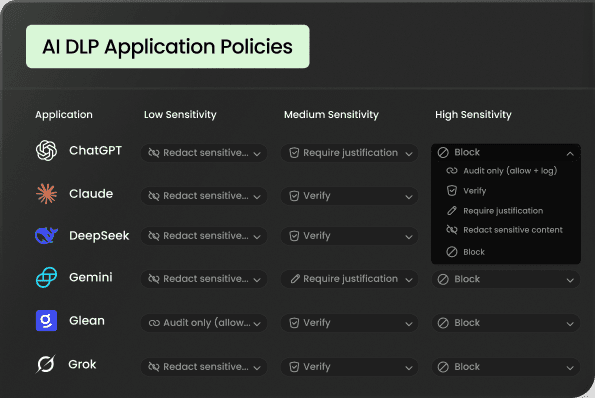
Block, warn, or require user justification before sensitive data is shared with AI. Apply granular policies based on data sensitivity, AI service, or user group.
Enable safe AI adoption
Allow employees to use AI safely while enforcing consistent data protection policies. Reduce risk without slowing productivity or innovation.
Audit every AI interaction
Capture AI interactions, policy decisions, blocked events, and user activity to support compliance, investigations, and security reporting.
AI Automated Remediation
Discovery and classification are the foundation. Enforcement is what makes governance real. When classification is right, enforcement becomes automatic — and the same signal governs both human access and AI behavior.
Four modes of coordinated enforcement.
Universal data labeling — the common language
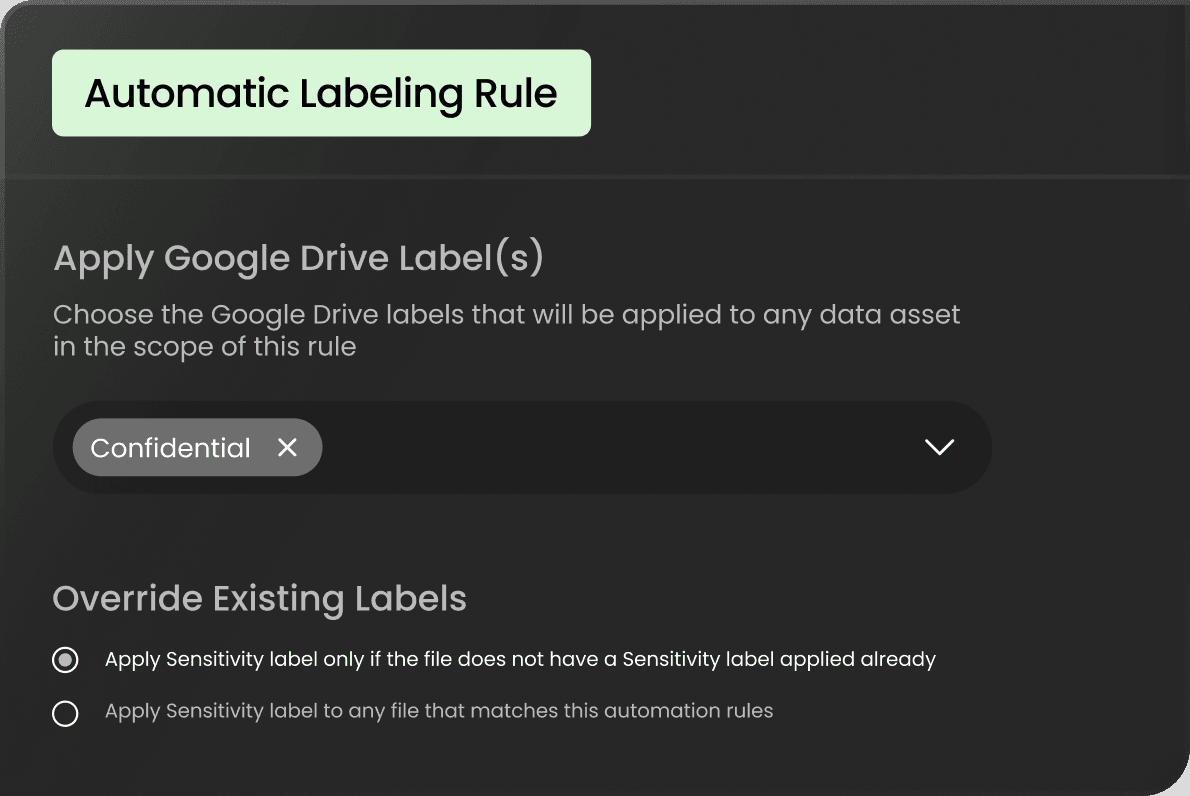
Labels applied and reconciled across all platforms—Microsoft 365, Google Workspace, cloud storage, data platforms. One signal drives every tool consistently.
Streamlined data, access, and identity remediation
When judgment is needed create contextual tickets, routed to data owners, with next steps. Drive ServiceNow, Jira, Slack, SIEM, SOAR. Outcomes, not alerts.
Consistent AI governance thru existing security stack
Policy violations auto-route to DLP, CASB/SSE, IAM, or SOAR to block, quarantine, or reroute. No new enforcement layer needed.
Continuous AI Compliance
All scanning and analysis runs in-environment, so you continuously meet compliance regulations while ensuring safe data operations — at any scale, without the cost becoming prohibitive.
Continuous compliance and responsible AI governance.
Continuous regulatory coverage
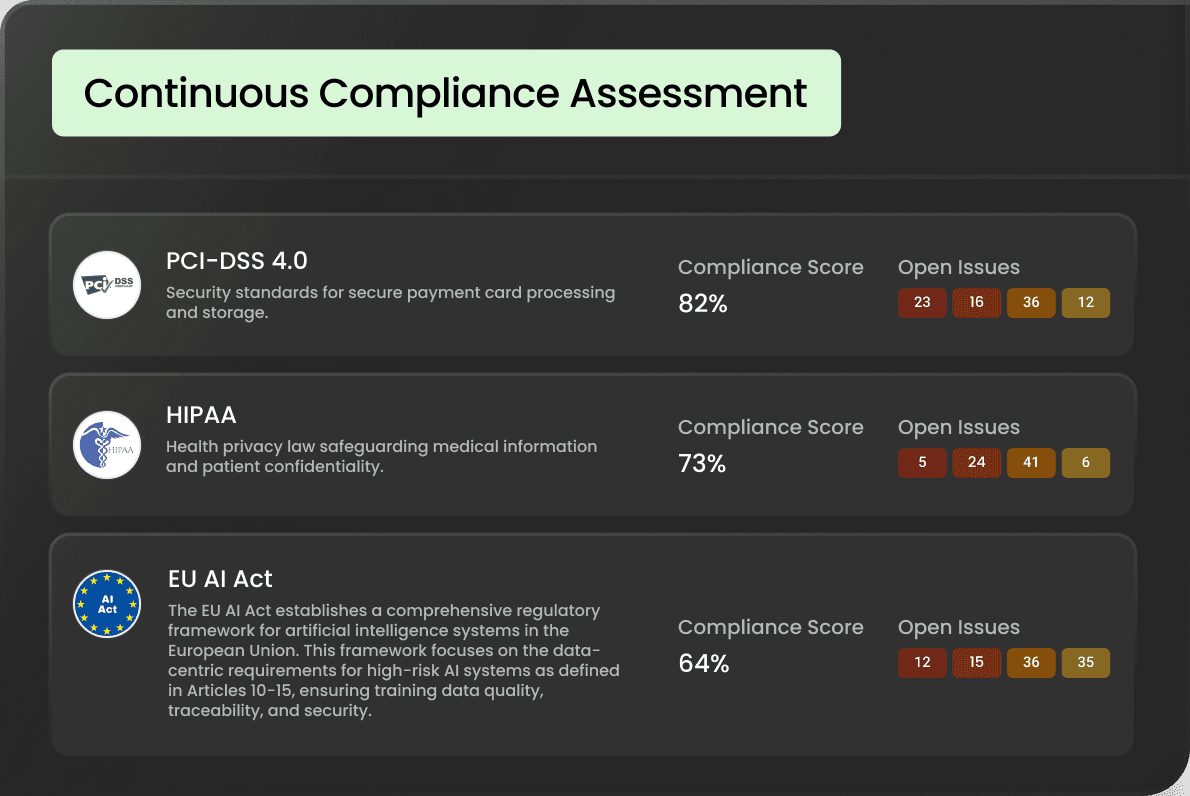
GDPR, HIPAA, PCI DSS, CCPA, SOC 2, ISO 27001, EU AI Act, NIST AI RMF, and emerging AI frameworks. Continuous proof, not point-in-time posture.
Automatic audit documentation
Audit trails for every dataset, classification decision, access event, and enforcement action—ready before regulators ask, not reconstructed after.
Complete data inventory
Risk-assessed and always current picture of entire data estate. Trustworthy and timely data insights for every AI stakeholder team.
Economics that sustain governance
$40,000 ops cost /year to scan 100 PB—10x cheaper than legacy means. Continuous governance becomes financially viable, not a budget fight at renewal.
Architecture that defines your AI data security
Scanning occurs in your environment and data never leaves it. Nothing to attest at audit—compliance is built into the architecture, not a layer on top.
How It Works
Sentra comes to your data. Your data never comes to Sentra.
Scanners Launch in Your Cloud
Short-lived, read-only scanners start inside your account, in the same region as the data. Nothing to install.
Discover and Classify
250+ built-in classifiers and AI models read the data on the scanner. Only labels and risk scores leave.
Map Access
Every sensitive asset is linked to the users, service accounts, applications and AI agents that can reach it.
Act Through Your Stack
Labels, tickets and access changes flow to Purview, DLP, IAM, SIEM and SOAR. Scanners shut down when done.
Works with Your Existing Stack.
Classification signals directly inform your existing Agentic AI, DLP, IAM, ITSM, SIEM, SOAR, and cloud platform controls—no parallel stack required.